TMCnet News
Sygnia Reveals New Activity by China-Nexus Threat Actor Fire Ant Targeting Trusted InfrastructureSygnia, the foremost global cyber readiness and response team, released the findings of their investigation into ongoing activity by a China-nexus threat actor, targeting key infrastructure that routes, authenticates, connects, and manages high-value environments. Tracked by Sygnia as 'Fire Ant', the adversary leveraged novel attack tools and methods to target Cisco IOS XR routers and turn them into operational platforms that suppress evidence of threat actor activity, collect traffic and credentials, and enable Fire Ant to explore other access points with the goal of spreading to other organizations. This press release features multimedia. View the full release here: https://www.businesswire.com/news/home/20260830433829/en/ 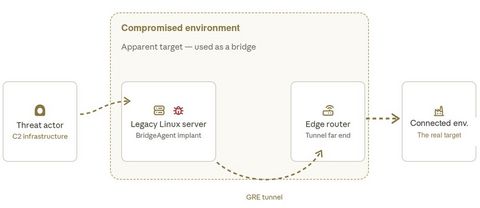
The threat actor reaches BridgeAgent on the legacy Linux server, where a GRE tunnel provides a pivot to the edge router and opens a route into a connected environment. The 2026 findings represent an evolution of Fire Ant's activity, expanding their focus beyond their 2025 activity of deep persistence within virtualization infrastructure targeting VMware ESXi and vCenter environments to strategic infrastructure abuse. "Fire Ant didn't just compromis systems. It compromised the trust layer those systems depend on. The routers, authentication servers, and management infrastructure many organizations overlook as legacy technology became the attacker's vantage point for reach, visibility, and control," said Asaf Perlman, Director of Incident Response at Sygnia. "That is what makes this research so important: the significance extended beyond the initially compromised environment, as the affected infrastructure could provide a path toward other connected high-value environments." Key findings of the threat report include:
The new intelligence value from Sygnia's investigation highlights a campaign targeting a highly interconnected environment where routers, TACACS servers and Linux management hosts were used as part of a broader access and collection layer. Fire Ant's interest in the compromised organization should be understood not only as an attempt to compromise a single environment, but as an effort to control infrastructure that may enable visibility, collection, and potential access beyond the immediate victim. Learn more about Fire Ant's 2026 activity in the latest threat research, "Fire Ant Evolves: From Hypervisors to Trusted Infrastructure." About Sygnia Sygnia is the world's foremost incident response and cyber readiness team. It applies creative approaches and bold solutions to each phase of an organization's security journey, meeting them where they are to ensure cyber resilience. Sygnia is the trusted advisor and service provider of leading organizations worldwide, including Fortune 100 companies. Sygnia is a Temasek company, part of the ISTARI Collective.
View source version on businesswire.com: https://www.businesswire.com/news/home/20260830433829/en/ |